
Yet despite growing awareness of cyber risk, many organisations still approach security as something that can be added later through software updates, network controls, or additional monitoring tools.
In reality, the most effective cyber security strategies begin long before a system is deployed. They begin at the design stage.
Historically, many operational technologies and physical security systems were designed with functionality as the primary objective.
Connectivity, interoperability, and operational performance often took precedence over cyber resilience.
As a result, organisations have frequently found themselves attempting to add security controls after systems have already been installed and integrated.
While these measures remain important, retrofitting cyber security can be complex, costly, and less effective than addressing risks during the design process.
Every additional workaround, compensating control, or network restriction increases operational complexity and can create new challenges for those responsible for managing systems day to day.
The Secure by Design approach recognises that cyber security should be considered throughout the entire lifecycle of a solution.
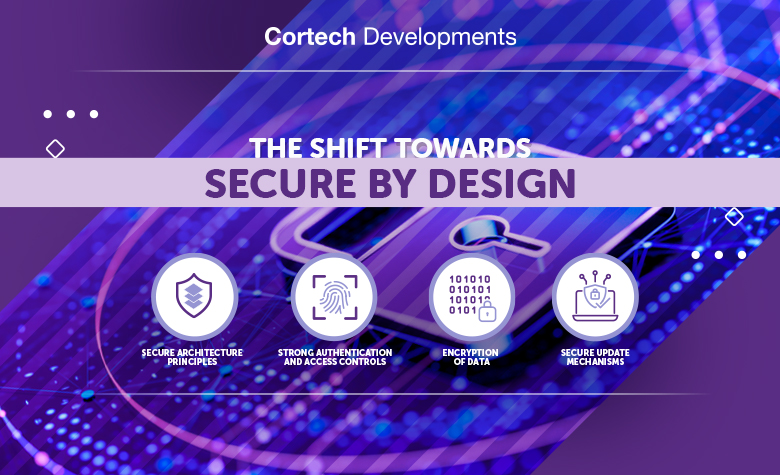
Rather than treating security as a separate requirement, it becomes an integral part of how systems are designed, developed, deployed, and maintained. This approach focuses on reducing risk from the outset through:
By embedding security into the design process, organisations can reduce exposure to common attack vectors while creating systems that are easier to manage and maintain over time.
For organisations operating critical services, cyber incidents can have consequences that extend beyond information security.
A successful attack may affect operational continuity, service delivery, safety, compliance, and public confidence.
The increasing convergence of physical security systems, operational technologies, and business systems means that cyber resilience can no longer be considered in isolation.
Every connected system becomes part of the wider operational risk landscape.
This is particularly relevant within sectors such as water, energy, healthcare, transport, and custodial services where system availability and resilience are essential.
One of the misconceptions surrounding cyber security is that stronger protection inevitably creates operational challenges.
In reality, well-designed security should support operational effectiveness rather than hinder it.
A Secure by Design approach seeks to balance protection with usability, ensuring that operators have secure access to the tools and information they need without introducing unnecessary complexity.
This is particularly important in environments where personnel must respond quickly to operational incidents and cannot afford delays caused by poorly implemented security controls.
Cyber threats will continue to evolve.
New vulnerabilities will emerge, technologies will change, and organisations will face increasing regulatory and operational requirements.
The most resilient organisations will be those that view cyber security not as a one-off project, but as a fundamental design principle.
By embedding security from the beginning, organisations can reduce risk, simplify management, and create a stronger foundation for future growth.
Ultimately, Secure by Design is about more than cyber security.
It is about creating operational environments that remain resilient, adaptable, and trusted in an increasingly connected world.
